01 / AI & SECURITY
MCP Access Control Studio
An AI agent can request a tool. The gateway decides whether it runs.
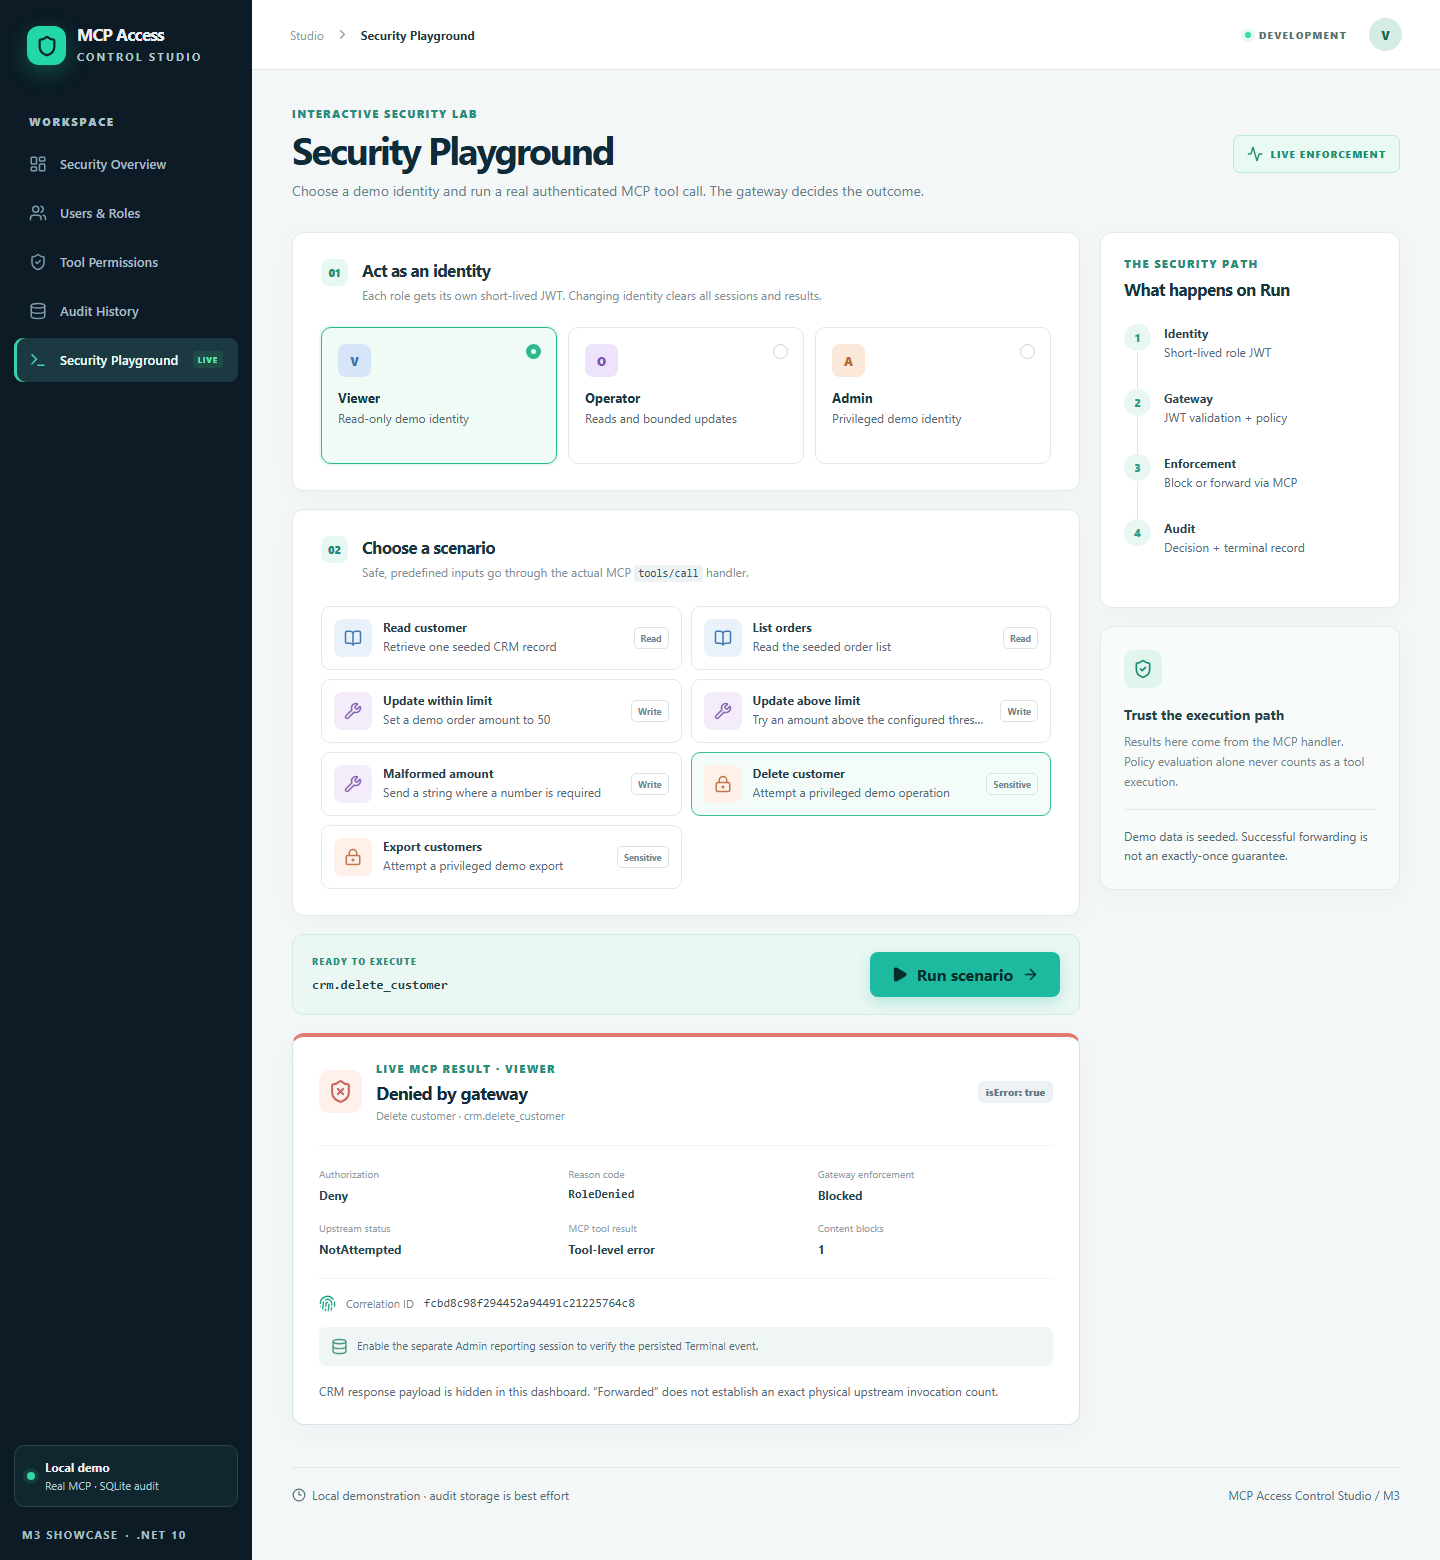
View the complete application screenshot
A real denied MCP call stops before it reaches the upstream tool.
01 / CONTEXT
The problem.
Giving an agent access to a tool catalog does not answer who may execute each tool. A useful authorization system also needs to explain its decisions and show what actually reached the upstream service.
02 / IMPLEMENTATION
The approach.
A local identity-aware MCP gateway paired with a React security dashboard. The Playground sends real authenticated MCP requests. Policy decisions and terminal outcomes are stored in SQLite and surfaced through an admin reporting API.
Simplified flow. Implementation details and boundaries are documented in the repository.
03 / TRADEOFFS
Decisions that matter.
Identity stays attached to the request
Viewer, Operator and Admin scenarios use their own short-lived JWTs. The separate reporting credential never replaces the selected execution identity.
Permissions live at the execution boundary
JWT validation, default-deny role rules and a conditional amount check run inside the MCP call handler before forwarding.
Audit records explain the outcome
Decision and Terminal records share a correlation ID. The dashboard reads persisted records and the same backend policy that enforces calls.
04 / EVIDENCE & BOUNDARIES
What was checked.
- Automated role and authorization regressions
- Real MCP SDK demo with persisted audit records
- Browser E2E scenarios for identity separation and outcomes
- Audit persistence verification across an API restart
Checks summarized from the project documentation. See the repository and CI for current details.
Scope of this reference project
Local reference demonstration with seeded identities and CRM data. No enterprise identity provider, tenant isolation or production deployment. Audit storage is best effort; allowed calls do not carry an exactly-once guarantee.
Run it locally
Follow the repository README for prerequisites and configuration before running:
node scripts/run-studio.mjsWORKING ON A SIMILAR PROBLEM?